Cybersecurity · 5 min read
Zero Trust Explained Without the Vendor Hype
Zero trust is not a product you can buy. It is a way of designing security for a world where users, devices and data are everywhere. Here is what it actually means, in plain English.
Few security terms have been stretched as far as "zero trust". Firewalls, identity platforms, endpoint tools and network products are all marketed as zero trust solutions. It is easy to come away thinking it is something you buy.
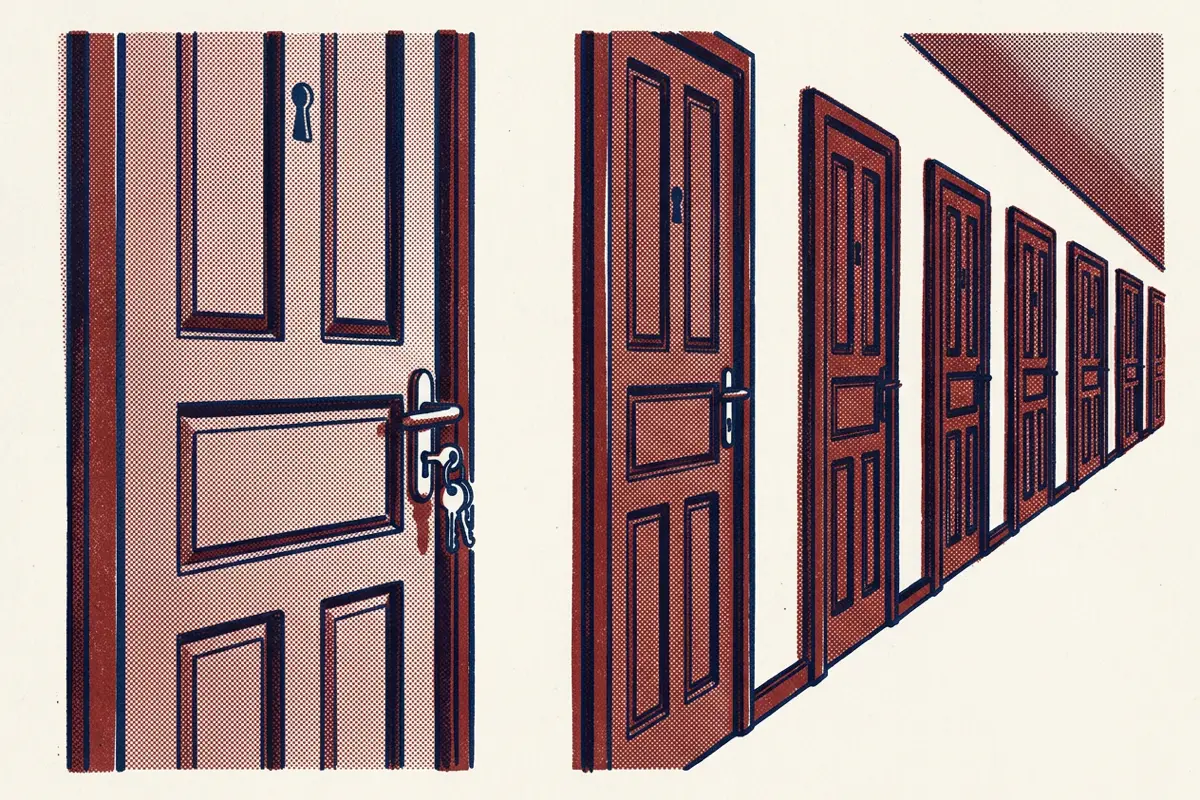
It is not. Zero trust is a design principle: never assume that a request is safe just because of where it comes from. Every request to access a system or piece of data should be verified on its own merits, using everything you know about who is asking, from what device, for what, and whether that makes sense right now.
This article explains what that means in practice, why the old approach stopped working, and how organisations actually move towards it.
The old model: a castle and a moat
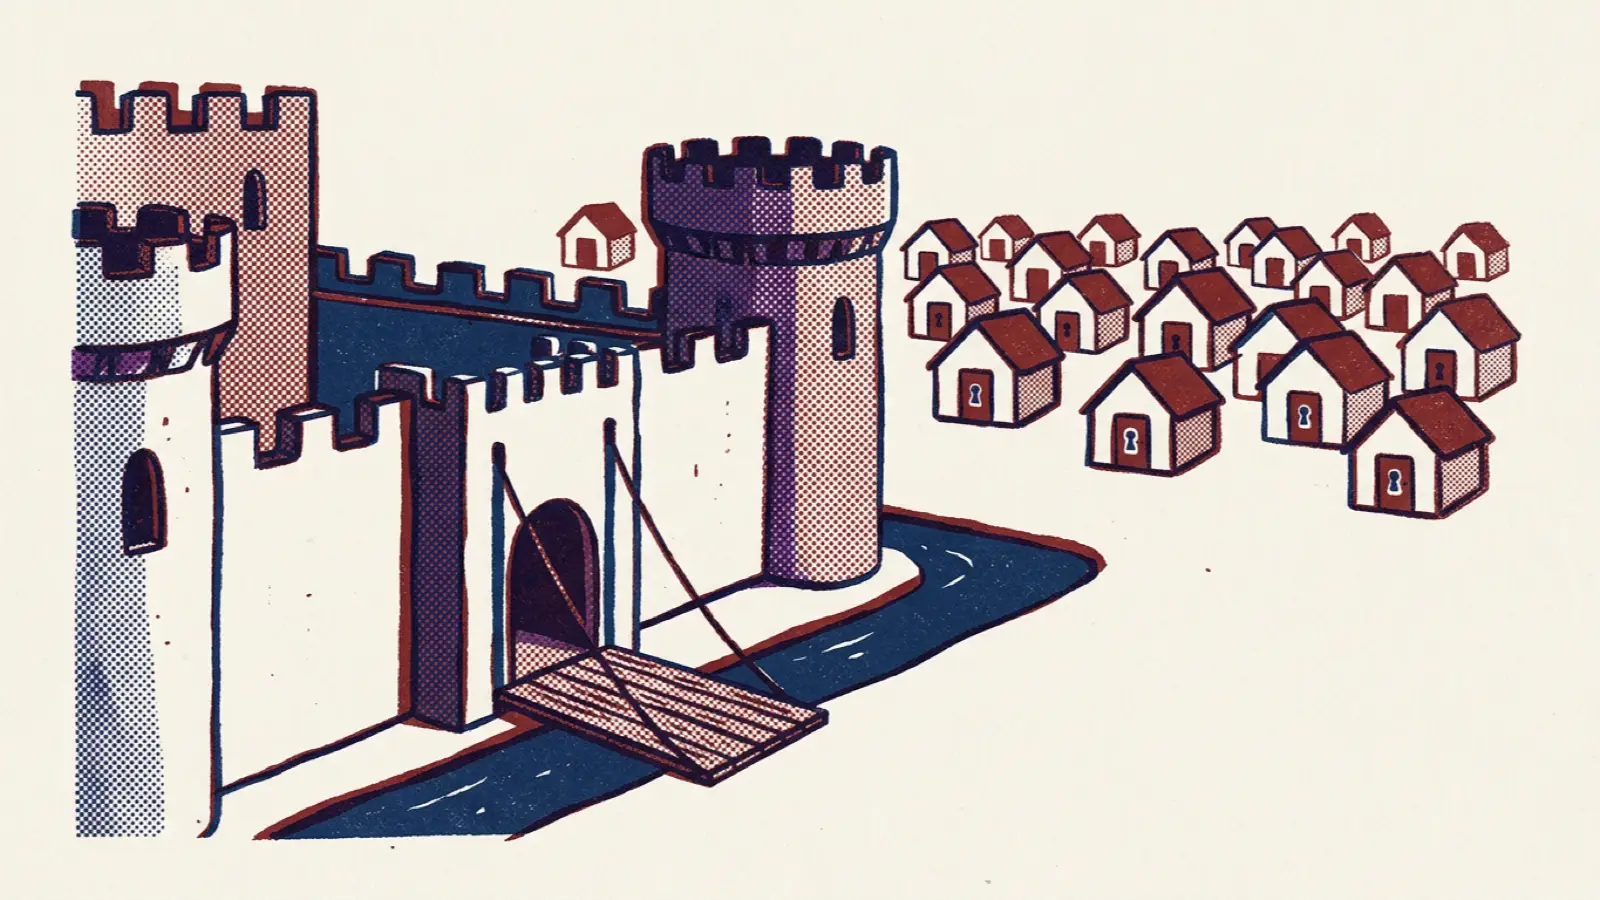
Traditional network security was built like a castle. A strong perimeter, firewalls and VPNs, kept outsiders out. Once you were inside, on the office network or connected through the VPN, you were largely trusted. You could reach most internal systems, and those systems trusted each other.
That model made sense when people worked in offices, applications ran in a company data centre, and devices were owned and managed by the organisation.
Why the castle stopped working
Several shifts undermined the perimeter:
- People work from anywhere. Home, client sites, cafés and airports are now normal places to work.
- Applications moved to the cloud. Many critical systems now run in cloud platforms and software-as-a-service products, outside the company network entirely.
- Devices vary. Personal phones, contractor laptops and shared devices all need some access.
- Attackers get inside. Phishing, stolen passwords and compromised suppliers mean that someone "inside" the network may well be an attacker. Once inside a flat network, they can often move freely.
When the network edge is everywhere and nowhere, defending it alone is not enough.
The core ideas of zero trust
Zero trust replaces the idea of a trusted inside with a few principles that apply to every request:
Verify explicitly
Every access decision considers the identity of the user, the health of the device, the location, the sensitivity of what is being accessed and whether the request fits normal behaviour. Being on a particular network does not grant trust on its own.
Give the least access needed
People and systems get access only to what they need, for as long as they need it. Broad standing access, especially administrator rights, is replaced with narrower, time-limited permissions.
Assume a breach
Design as if an attacker is already inside. Segment networks and systems so that compromising one does not open the door to everything, and monitor activity so unusual behaviour is spotted quickly.
What it looks like in practice
Zero trust is usually built in layers over several years. The common building blocks are:
- Strong identity. A single, well-governed identity system for staff, with multi-factor authentication everywhere and phishing-resistant methods for high-risk access. Identity becomes the main control point.
- Device trust. Devices must meet basic health requirements, such as being managed, encrypted and up to date, before they can reach sensitive resources.
- Application-level access. Instead of putting users on the network through a VPN, each application is reached through a gateway that checks identity and device for every connection.
- Segmentation. Networks and workloads are divided so that systems can only talk to the systems they need to.
- Data protection. Sensitive data is classified, and access rules follow the data, wherever it is stored.
- Visibility and automation. Logs from identity, devices, networks and applications are brought together, so suspicious activity can be detected and, where appropriate, access revoked automatically.
Where to start
Because zero trust is a journey, the first steps matter most. For most organisations they are:
- Get identity right. Consolidate identity systems, enforce multi-factor authentication for all users and remove shared accounts. This alone closes many of the most common attack routes.
- Reduce standing privileges. Inventory administrator accounts, remove those that are not needed, and move towards just-in-time elevation for the rest.
- Protect your most important applications first. Put your crown-jewel systems behind identity-aware access before tackling everything else.
- Know your devices. You cannot make decisions about device health if you do not know what devices are connecting.
Identity is so central to zero trust that it is worth assessing separately. The Identity & Access Management assessment looks at joiners, movers and leavers, privilege governance, authentication, non-human identities such as service accounts, access reviews and directory architecture.
Common misconceptions
- "We bought a zero trust product, so we're done." Products can help with specific layers, but zero trust depends on how they are configured and governed together.
- "Zero trust means trusting nobody." It means trust is earned for each request based on evidence, rather than assumed from location. Day-to-day work should become smoother, not harder, as single sign-on and better device management reduce friction.
- "It's only for large enterprises." Smaller organisations can adopt the principles, starting with strong identity, managed devices and cloud applications protected by multi-factor authentication.
- "It's a network project." Networks are one part. Identity, devices, applications and data matter just as much.
How mature is your approach?
The Zero Trust Security assessment covers six areas: identity and access, network segmentation, device trust, data protection, visibility and analytics, and governance and automation. Most organisations find they are further ahead in some areas, often identity, than others, such as segmentation or data classification. That uneven profile is normal, and it tells you where to invest next.
Frequently asked questions
Does zero trust replace VPNs?
Over time, often yes. Many organisations move from network-level VPN access to application-level access through identity-aware gateways. In practice, VPNs and newer approaches often run side by side for several years.
How long does a zero trust programme take?
Meaningful progress, such as strong identity and protection for key applications, can be made within a year. A full transition typically takes several years, because it touches identity, devices, networks, applications and data.
Is zero trust a standard?
It is a set of principles rather than a single standard, although several governments and standards bodies publish guidance on zero trust architecture. Those documents are useful references when planning your approach.